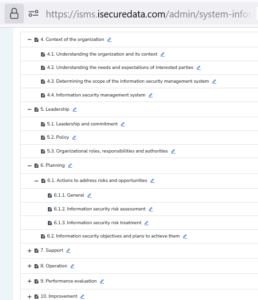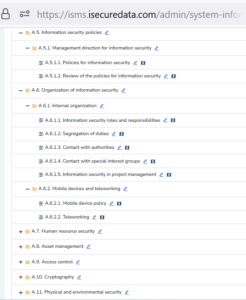
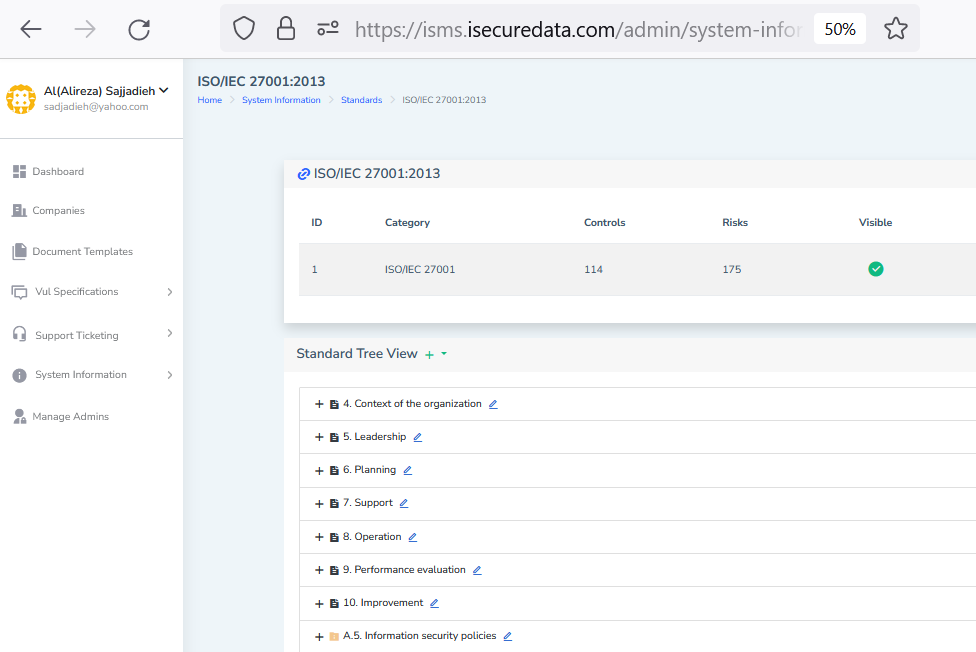
The adoption of information security management systems (ISMS) is crucial for safeguarding sensitive data and ensuring the resilience of organizations against evolving cyber threats. ISO 27001 serves as a gold standard for ISMS implementation, and in this guide, we’ll explore how to effectively implement ISO 27001 in a startup, small, or medium-sized company. iSecureData Copilot, a cutting-edge SaaS platform, will play a central role in simplifying and optimizing the entire implementation process. iSecureData Copilot provides all the necessary customosable templates, policies, samples and forms for implementing ISO 27001.
Phase 1: Establishing the ISMS
Activities:
- Leadership Commitment:
- Demonstrate top management commitment to information security.
- Engage in leadership discussions to emphasize the importance of ISO 27001 compliance.
- Define Scope and Objectives:
- Clearly articulate the scope and objectives of the ISMS.
- Utilize iSecureData Copilot to document and communicate the scope with stakeholders.
- Establish a Governance Structure:
- Formulate a governance structure defining roles and responsibilities.
- Leverage iSecureData Copilot to create a centralized repository for governance documentation.
iSecureData Copilot Usage:
- Platform Dashboard:
- Monitor progress and adherence to milestones.
- Access governance documentation and communicate responsibilities.
Phase 2: Risk Assessment and Treatment
Activities:
- Asset Identification:
- Identify and categorize organizational assets.
- Collaborate with teams to ensure comprehensive asset identification.
- Risk Analysis:
- Conduct a thorough risk assessment using the iSecureData Copilot platform.
- Engage relevant teams in the risk analysis process.
- Controls Implementation:
- Map ISO 27001 controls to identified risks.
- Leverage iSecureData Copilot’s risk mapping feature for a seamless implementation process.
iSecureData Copilot Usage:
- Risk Analysis Module:
- Use the platform for systematic risk identification and assessment.
- Map controls to identified risks within the platform.
Phase 3: Implementation of Controls
Activities:
- Policy Development:
- Develop and communicate information security policies.
- Utilize iSecureData Copilot’s policy templates for efficient policy development.
- Training and Awareness:
- Conduct training sessions on security policies and best practices.
- Leverage iSecureData Copilot to disseminate training materials and track completion.
iSecureData Copilot Usage:
- Policy Management:
- Customize policy templates within the platform.
- Utilize the platform for tracking employee completion of training sessions.
Phase 4: Monitoring and Measurement
Activities:
- Incident Response Planning:
- Develop incident response plans and procedures.
- Engage with relevant teams to ensure a well-coordinated response.
- Performance Metrics Definition:
- Define key performance indicators (KPIs) for monitoring ISMS effectiveness.
- Collaborate with teams to establish measurable KPIs.
iSecureData Copilot Usage:
- Incident Handling Forms and Playbooks:
- Leverage incident handling forms and playbooks within the iSecureData Copilot platform for structured response.
- Utilize the platform’s dashboard for real-time monitoring of key performance metrics.
Phase 5: Continuous Improvement
Activities:
- Internal Audits:
- Conduct regular internal audits to ensure compliance.
- Collaborate with internal audit teams to address findings.
- Management Review:
- Conduct periodic management reviews of the ISMS.
- Utilize iSecureData Copilot for generating detailed reports for management review meetings.
iSecureData Copilot Usage:
- Audit Reporting Module:
- Document and track internal audit findings within the platform.
- Generate comprehensive reports in the platform for management reviews.
Conclusion
Implementing ISO 27001 is a strategic investment in the resilience of an organization’s information security. iSecureData Copilot acts as a catalyst, streamlining the implementation process and providing CEOs with a centralized platform for oversight. By leveraging the platform’s features across each phase, CEOs can ensure a seamless and effective ISMS implementation. Continuous monitoring, employee engagement, and collaboration across teams will be key to sustaining a culture of security within the organization. iSecureData Copilot facilitates this journey, ensuring a robust ISMS that aligns with ISO 27001 standards.